

On January 8, 2026, the California Privacy Protection Agency (“CalPrivacy”) announced an enforcement action against Rickenbacher Data LLC (d/b/a “Datamasters”), an information reseller, for failing to register as a data broker under the California Delete Act. Datamasters agreed to pay
Latest from Inside Privacy - Page 12
UNESCO Adopts First Global Framework on Neurotechnology Ethics
On November 12, 2025, UNESCO’S General Conference adopted its Recommendation on the Ethics of Neurotechnology (“the Recommendation”)–the first attempt at establishing a global legal framework for the ethical development and use of neurotechnology. The Recommendation aims to set out a
Germany Transposes NIS 2 Directive – Increased Cybersecurity Requirements for Businesses
On 5 December 2025, the Act Transposing the NIS 2 Directive and Regulating Key Aspects of Information Security Management in the Federal Administration (Gesetz zur Umsetzung der NIS-2-Richtlinie und zur Regelung wesentlicher Grundzüge des Informationssicherheitsmanagements in der Bundesverwaltung (“NIS2UmsG”) (see
FTC Sets Aside Rytr Final Order Pursuant to White House AI Action Plan

On December 22, the Federal Trade Commission (“FTC”) issued an order setting aside its 2024 final consent order against Rytr, LLC (“Rytr”) on the grounds that the facts alleged in the Rytr complaint did not violate Section 5. The Commission
German Government Proposes GDPR Reform to Shift Responsibility to Manufacturers
On December 4, 2025, the German Federal Government published its Federal Modernization Agenda, setting out a series of suggested amendments to the GDPR and the Federal Data Protection Act (Bundesdatenschutzgesetz). Among the key measures, Germany seeks to shift certain
FTC Issues Warning Letters for Violations of Consumer Reviews Rule

The Federal Trade Commission (FTC) sent letters to 10 companies—whose identities were not publicly disclosed—on December 22, 2025, warning them about potential violations of the Consumer Reviews Rule. The Rule, which took effect in October 2024, targets deceptive online review
FTC Announces 10-Year Information Security Consent Orders with Illuminate Education and Illusory Systems
The Federal Trade Commission (FTC) recently announced that it agreed to proposed consent orders with two companies that experienced recent cybersecurity incidents, Illuminate Education (“Illuminate”) and Illusory Systems, which does business as Nomad (“Illusory”), to resolve allegations that both companies’
NIST Publishes Preliminary Draft of Cybersecurity Framework Profile for Artificial Intelligence for Public Comment
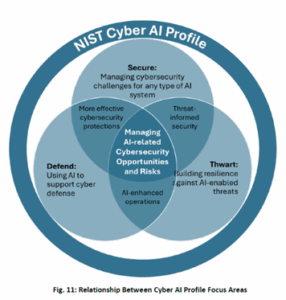
On December 16, 2025, the U.S. National Institute of Standards and Technology (“NIST”) published a preliminary draft of the Cybersecurity Framework Profile for Artificial Intelligence (“Cyber AI Profile” or “Profile”). According to the draft, the Cyber AI Profile is intended
California AG Announces $1.4 Million Settlement with Mobile App Gaming Developer Over CCPA Violations
On November 21, 2025, California Attorney General Rob Bonta announced a $1.4 million settlement with Jam City, Inc. (“Jam City”), a mobile app gaming company, for alleged violations of the California Consumer Privacy Act (“CCPA”) and Unfair Competition Law (“UCL”).
CISA Releases Cybersecurity Performance Goals 2.0 for Critical Infrastructure
On December 11, 2025, the U.S. Cybersecurity and Infrastructure Security Agency (“CISA”) released its Cybersecurity Performance Goals 2.0 (“CPG 2.0”), an update to its core set of recommended cybersecurity practices for critical infrastructure owners and operators, which we previously wrote