
California’s CCPA cybersecurity audits begin in 2027, with new requirements for covered businesses, annual audits, certifications, and reporting.

California’s CCPA cybersecurity audits begin in 2027, with new requirements for covered businesses, annual audits, certifications, and reporting.
The EU Cyber Resilience Act (CRA) makes cybersecurity a prerequisite for access to the EU market, not only for hardware products with digital elements, but also for software placed on the market independently. Its core requirements are far-reaching: conformity assessments,
Proposed FCC TCPA changes would narrow revoke-all requirements, allow exclusive opt-out methods, and expand exemptions.
GT Data Privacy & Cybersecurity shareholders Ian C. Ballon, Timothy A. Butler, and David A. Zetoony were recognized in the 2027 edition of The Best Lawyers in America®.
This GT Alert summarizes the state-law developments and highlights practical compliance considerations for businesses that develop, sell, or use algorithmic pricing tools.
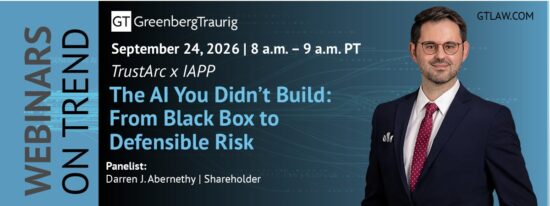
IAPP will host the webinar “The AI You Didn’t Build: From Black Box to Defensible Risk” on Sept. 24 from 8 to 9 a.m. PT. The program will focus on the risks associated with artificial intelligence embedded in third-party software
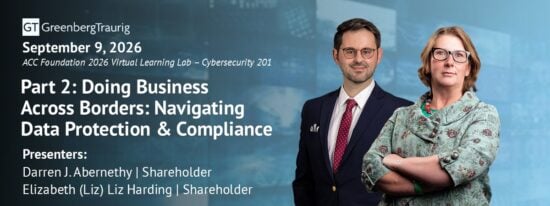
Greenberg Traurig Shareholders Darren Abernethy and Liz Harding will present during the ACC Foundation’s Cybersecurity 201 Virtual Learning Labs on Sept. 9, 2026.
FTC seeks public comment on a proposed policy statement addressing personalized pricing and how the FTC Act Section 5 may apply to data-driven pricing practices.
Vermont joins the Consortium of Privacy Regulators, expanding multistate privacy enforcement coordination among state regulators.
On July 10, 2026, New York City Department of Consumer and Worker Protection (DCWP) finalized and adopted its “Click-to-Cancel Rule,” which takes effect on Oct. 1, 2026.